CMMC 2.0
Understanding the Cybersecurity Maturity Model Certification and Why It Matters
Contents
Introduction
Why CMMC 2.0 Awareness Matters
Cybersecurity is no longer just a concern for IT teams; it’s a requirement for doing business with the U.S. Department of Defense (DoD). With sensitive government data increasingly targeted by cybercriminals and nation-state adversaries, the Cybersecurity Maturity Model Certification (CMMC) was developed to enforce baseline cybersecurity practices across the defense supply chain.
In 2021, the DoD introduced CMMC 2.0, an updated and simplified version of the framework, designed to strengthen national security while reducing compliance burdens for small and mid-sized contractors.
At Data Collaboration Services (DCS), we are well aware of CMMC 2.0 requirements and align our IT infrastructure management, risk assessments, and security consulting with its principles. While we are not a certification body, we can help clients understand the framework, prepare for third-party assessments, and strengthen their security posture in line with DoD expectations.
What is CMMC 2.0?
The Cybersecurity Maturity Model Certification (CMMC) is a framework developed by the DoD to ensure that contractors and subcontractors handling Controlled Unclassified Information (CUI) or Federal Contract Information (FCI) meet strict cybersecurity standards.
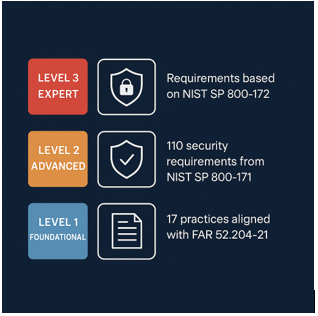
CMMC 2.0, announced in November 2021, builds on the original framework but introduces key simplifications:
Three Levels of Maturity (down from five):
- Level 1 (Foundational): Basic safeguarding aligned with Federal Acquisition Regulation (FAR) 52.204-21.
- Level 2 (Advanced): Aligned with NIST SP 800-171 (110 security controls).
- Level 3 (Expert): Based on NIST SP 800-172, for the most sensitive DoD programs.
Reduced Complexity: Contractors no longer need certification for all five levels. Instead, requirements align more closely with NIST standards, which most defense contractors already recognize.
Self-Assessments Allowed (for some): Certain Level 1 and some Level 2 contractors can complete annual self-assessments instead of third-party audits, lowering the compliance cost.
Why CMMC 2.0 Matters for Your Business
If your organization does business with the DoD, directly or indirectly, CMMC 2.0 compliance is essential.
Here’s why it matters:
- DoD Requirement: By 2026, CMMC 2.0 will be a contractual requirement in all new DoD solicitations.
- Protecting National Security: Compliance ensures sensitive data (CUI and FCI) isn’t exposed to cyber threats.
- Competitive Advantage: Companies aligned with CMMC 2.0 will qualify for more DoD contracts.
- Customer Trust: Demonstrates that your business takes cybersecurity seriously, building credibility with clients, partners, and regulators.
- Avoiding Legal/Financial Risks: Non-compliance could mean losing contracts, reputational harm, and potential penalties.
Did you know?
According to the DoD, over 300,000 contractors will need to comply with CMMC 2.0 in the coming years.
Breaking Down the Three Levels of CMMC 2.0
Level 1: Foundational (Basic Cyber Hygiene)
- Who it applies to: Businesses handling Federal Contract Information (FCI) only.
- Requirements: 17 basic practices from FAR 52.204-21.
- Assessment: Annual self-assessment with affirmation from a company executive.
Examples: Small subcontractors providing commercial products or services to DoD contractors.
Level 2: Advanced (NIST SP 800-171)
- Who it applies to: Businesses handling Controlled Unclassified Information (CUI).
- Requirements: 110 practices from NIST SP 800-171 across 14 families (e.g., access control, incident response, encryption).
- Assessment:
- Critical Programs: Third-party assessments every three years.
- Non-critical Programs: Annual self-assessments allowed.
Examples: Contractors developing defense software or maintaining sensitive defense systems.
Level 3: Expert (NIST SP 800-172)
- Who it applies to: Businesses working on the most critical national security programs.
- Requirements: Advanced cybersecurity practices based on NIST SP 800-172.
- Assessment: DoD-led assessments (no self-assessment allowed).
Examples: Companies working on advanced defense technologies or mission-critical DoD operations.
How DCS Can Support Businesses with CMMC 2.0 Awareness
While DCS is not a CMMC certifying body, we can guide our clients in aligning their IT systems and data protection practices with CMMC 2.0 principles.
Here’s how:
CMMC Readiness Assessments
- Review your IT systems against CMMC requirements.
- Identify gaps in controls, policies, and documentation.
NIST Alignment
- Since CMMC 2.0 is built on NIST standards, DCS helps map your controls to NIST SP 800-171 and NIST SP 800-172 practices.
Data Mapping & Risk Management
- Ensure visibility into where FCI and CUI reside.
- Implement risk management practices aligned with DoD expectations.
Implementing Security Controls
- Access management, encryption, network monitoring, and logging.
- Multi-factor authentication and zero-trust architectures.
Consulting & Documentation
- Assist in preparing for third-party assessments by aligning policies, incident response plans, and documentation with CMMC standards.
Training & Awareness
- Conduct cybersecurity training to build a security-first culture across your workforce.
Benefits of Aligning with CMMC 2.0
- Stronger Cybersecurity Posture: Protects your organization from breaches and ransomware.
- Contract Eligibility: Stay competitive in the DoD supply chain.
- Simplified Compliance: Aligning with NIST standards makes regulatory overlap easier (GDPR, HIPAA, etc.).
- Reduced Risk Exposure: Mitigate insider threats, vendor risks, and third-party vulnerabilities.
- Customer Trust & Brand Reputation: Demonstrates proactive investment in cybersecurity.
Industry Use Cases
- Defense Contractors: Meet DoD requirements for CUI protection.
- Manufacturing: Secure defense supply chains and industrial control systems.
- Technology Providers: Protect sensitive defense software and cloud environments.
- Logistics & Support Services: Secure networks that handle sensitive DoD logistics data.
Takeaway
CMMC 2.0 isn’t just another compliance framework; it’s a gateway to doing business with the Department of Defense. With increasing cyber threats targeting national defense, the DoD is raising the bar for cybersecurity across its supply chain.
At Data Collaboration Services (DCS), we align our IT infrastructure and security practices with CMMC 2.0 principles, helping clients assess risks, implement controls, and prepare for certification readiness.
If your business is part of the DoD supply chain or plans to enter it, now is the time to prepare. Aligning with CMMC 2.0 not only protects your data but also positions your business for long-term growth and credibility.
To know how we can help your organization prepare for CMMC 2.0, contact us.
Frequently Asked Questions (FAQ's)
CMMC 2.0 is the Department of Defense’s updated cybersecurity framework that requires defense contractors to implement specific security practices depending on the sensitivity of the information they handle.
All DoD contractors and subcontractors handling FCI or CUI, regardless of size.
Full implementation is expected by 2026, but businesses should begin preparation now.
CMMC 2.0 reduces levels from 5 to 3, aligns directly with NIST standards, and allows self-assessments for some contractors.
Yes, but not all levels require third-party certification. Some Level 1 and Level 2 contractors can complete annual self-assessments.
Non-compliance may result in loss of eligibility to bid on or retain DoD contracts.
While not a certifying body, DCS helps clients align IT infrastructure and security controls with CMMC 2.0 requirements, conduct readiness assessments, and prepare for third-party audits.
Yes. It closely aligns with NIST SP 800-171, and also supports compliance efforts for HIPAA, GDPR, ISO 27001, and other standards.